
aiDAST360
Test like an attacker, no source code needed
Combines OWASP ZAP, Nuclei and 80+ custom checks across OWASP Top 10, API Security Top 10 and GraphQL business-logic testing.
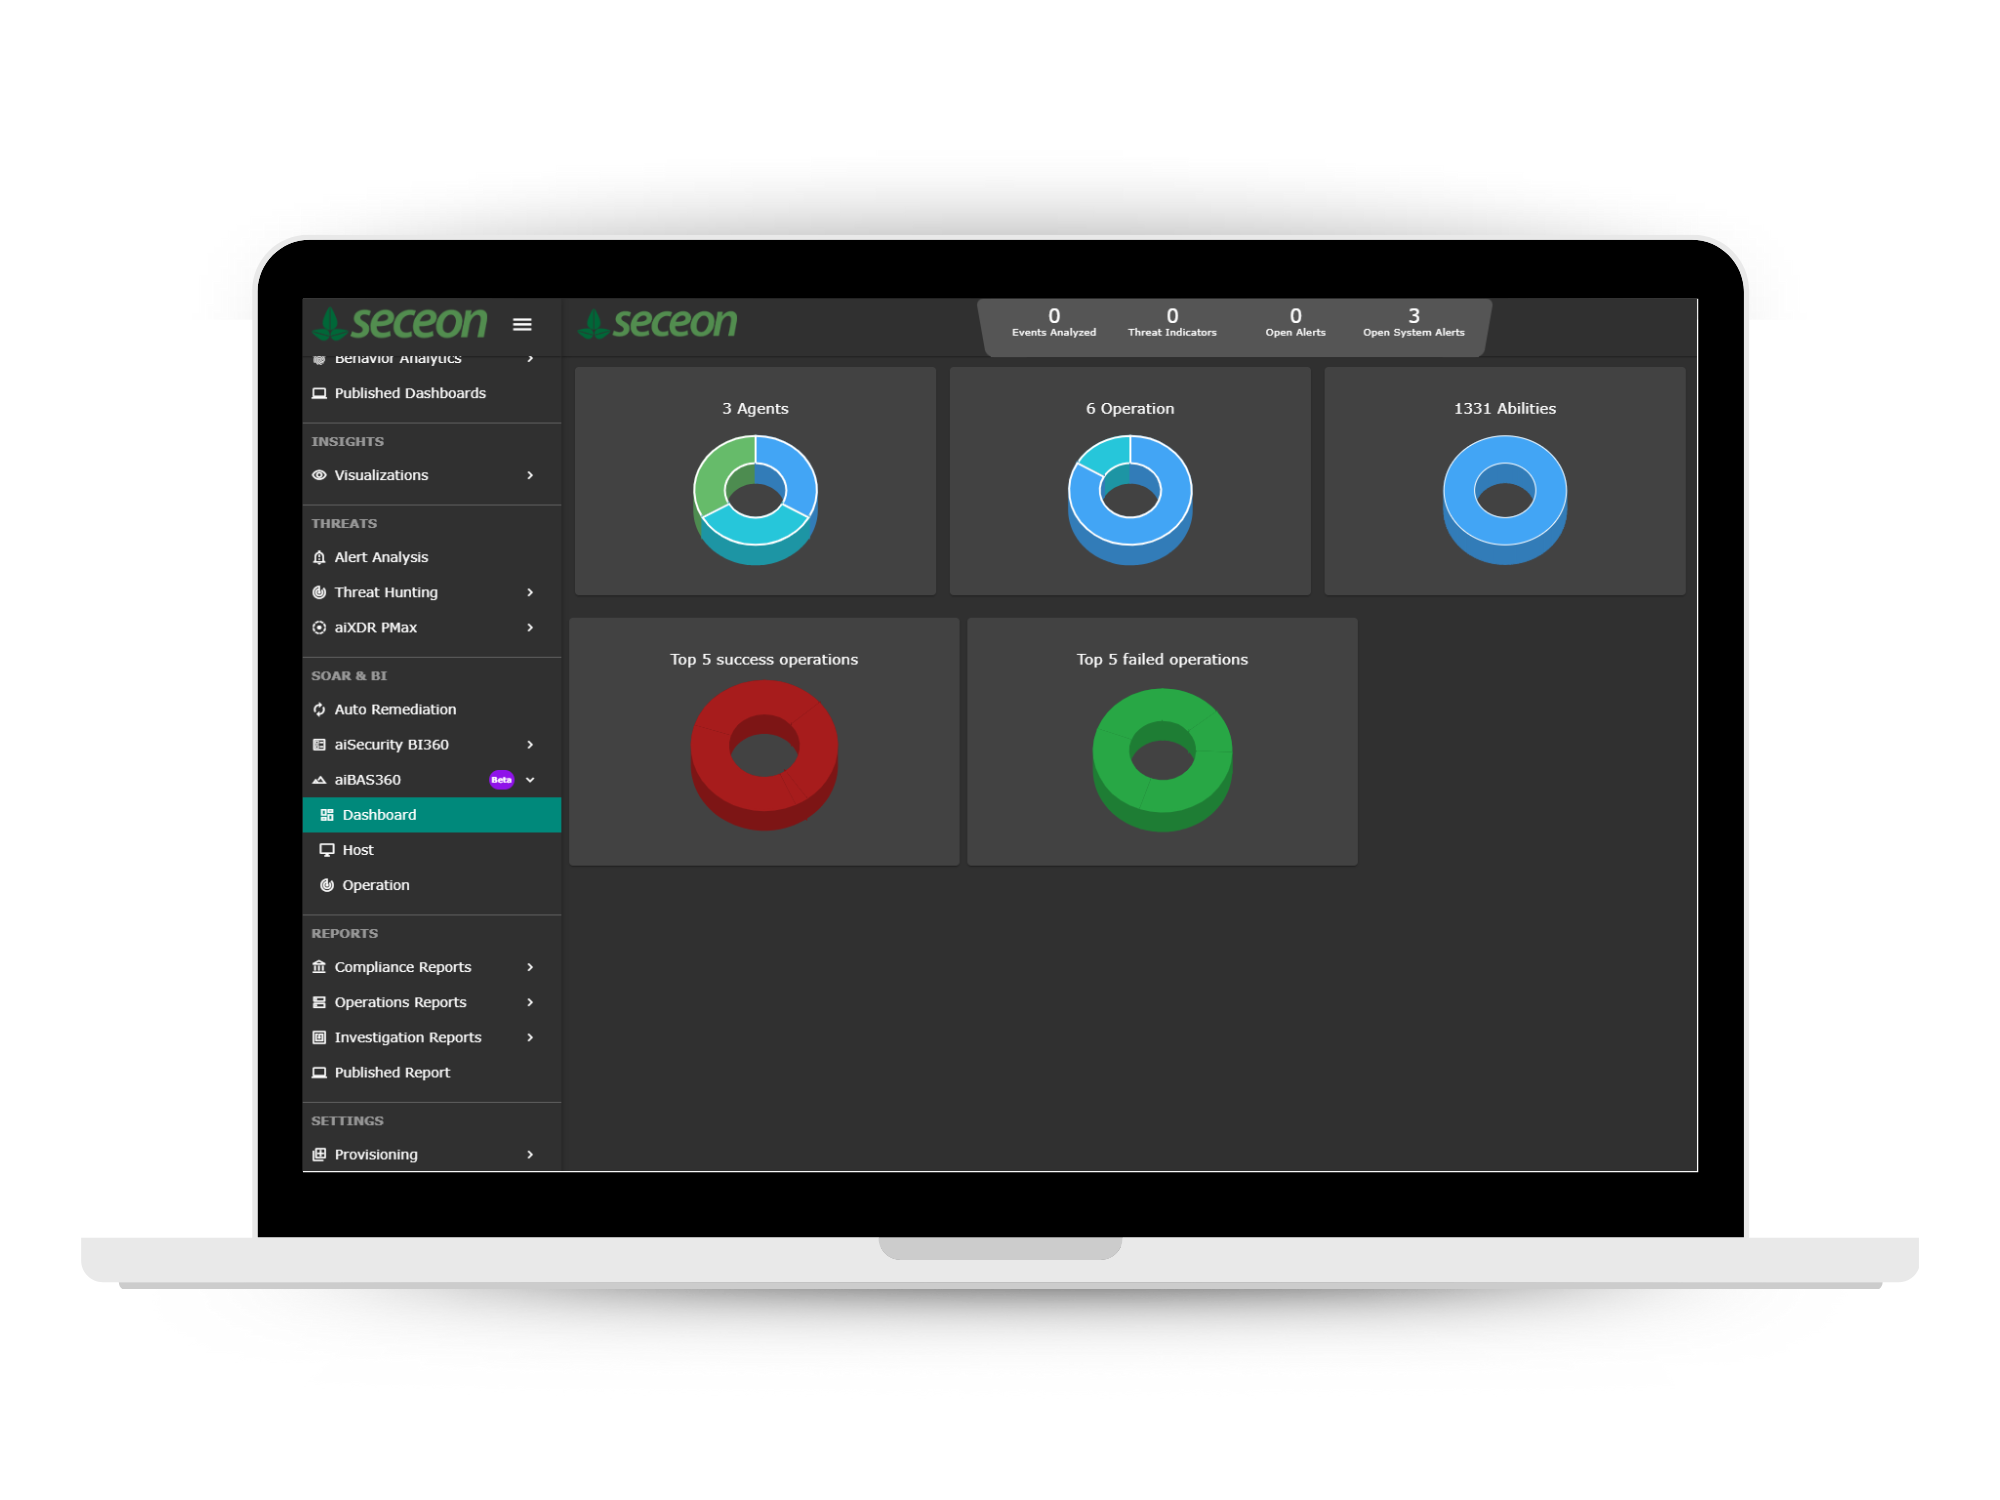
Illustrative example of scan findings.
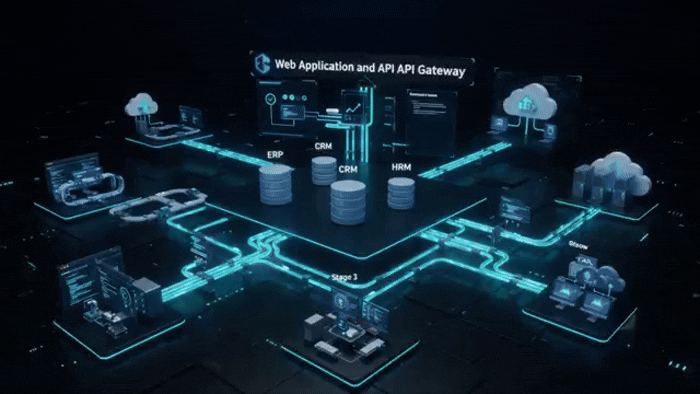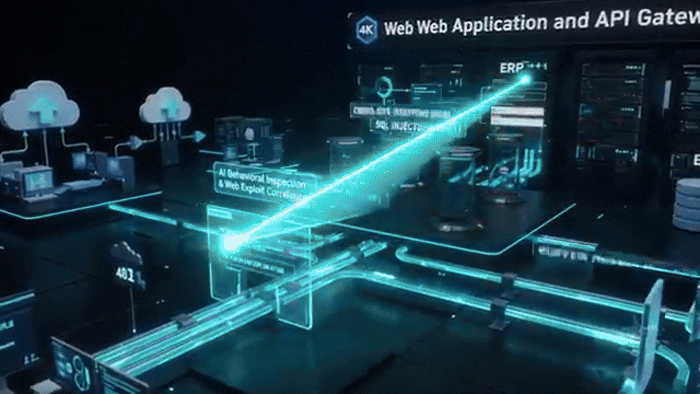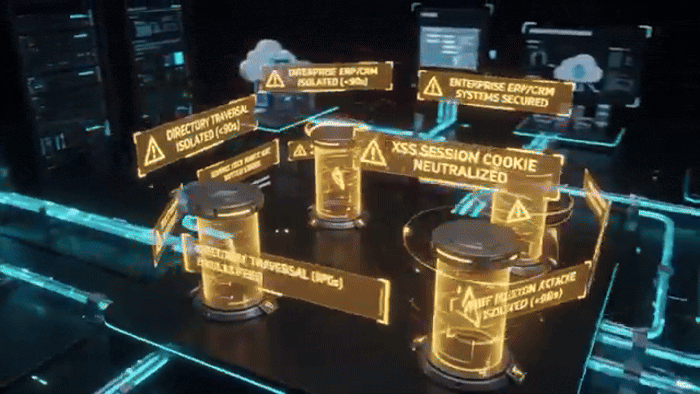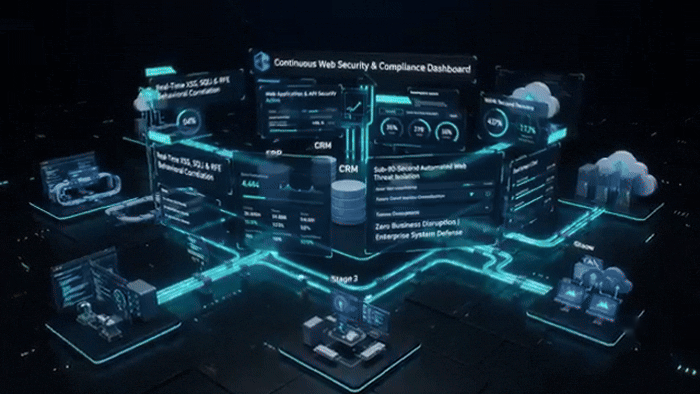
Seceon’s Web Application Security delivers comprehensive protection against threats targeting web applications, ensuring continuous monitoring and defense against vulnerabilities and attacks.
Book a demo
Modern web applications often consist of numerous components, including third-party libraries, APIs, and microservices, each of which can introduce potential vulnerabilities.
While these practices enhance agility, they can also lead to security being overlooked or poorly integrated, resulting in vulnerabilities slipping through the cracks.
Legacy systems that are no longer supported or have unpatched vulnerabilities can be difficult to secure, yet they often remain in use due to cost or compatibility reasons.
Continuous dynamic testing of web applications and APIs, plus runtime exploit detection, on one platform.
aiDAST360
Combines OWASP ZAP, Nuclei and 80+ custom checks across OWASP Top 10, API Security Top 10 and GraphQL business-logic testing.
Illustrative example of scan findings.
Scan profiles
From a rapid smoke test for change validation to maximum crawl depth and active testing.
Authenticated scanning
10+ authentication methods, with an encrypted credential vault.
Evidence and fixes
Request and response evidence, CVSS v3 scoring, CWE mapping and remediation code snippets.
Accuracy
ML-assisted false-positive reduction, with an analyst feedback loop and periodic auto-retraining.
Potential Web Exploit alert
aiSIEM flags web exploit activity, including attempts that behave differently from WAF protections such as Akamai.
Attack surface and correlation
ASM asset sync triggers testing automatically on new web and API assets. Findings stream to aiSIEM for threat correlation, mapped to MITRE ATT&CK T1190.
Compliance and reporting
Automated control mapping, PDF compliance reports, finding aging and SLA reports, and JSON or CSV export for ticketing and GRC.
Deployment
Deployed on-premises on Seceon CCE with full air-gapped support. Built for MSSPs with multi-tenancy, scheduled recurring scans and a cross-tenant risk dashboard.
Discover how organizations identify web application vulnerabilities, detect web attacks, and strengthen security with Seceon.
Web application security protects websites, APIs, and online services against attacks that exploit weaknesses in application code, configuration, or design. Without effective protection, attackers may steal credentials, access sensitive data, or execute malicious code. Seceon helps security teams detect web exploit indicators through its aiSIEM and aiXDR capabilities, supporting investigation and response to suspicious activity.
Security teams can monitor suspicious application requests, unexpected database activity, and attempts to inject scripts into web pages. Secure coding, input validation, and application testing are also important preventive measures. Seceon's aiSIEM and aiXDR can help detect indicators associated with web exploits, including SQL injection and cross-site scripting, so teams can investigate potentially malicious activity.
Directory traversal attempts may try to access files outside an application's intended directories, while remote code execution can allow attackers to run code on a vulnerable system. Detection can involve monitoring suspicious file paths, unexpected process execution, abnormal application behavior, and related security events. Seceon's web application security capabilities use aiSIEM and aiXDR to help identify indicators associated with these and other web exploit attack vectors.
Outdated software may contain known vulnerabilities, while APIs and third-party components can introduce additional weaknesses into an application. Organizations should inventory software components, apply security patches, test applications regularly, and monitor for suspicious activity. Seceon's security analytics can help identify indicators of exploitation, complementing secure development and vulnerability management practices.
Vulnerability scanning looks for weaknesses that attackers might exploit. Real-time threat detection monitors security events and activity for signs that an attack may be underway. Both are important: scanning helps teams identify issues to fix, while threat detection helps them investigate exploitation attempts. Seceon provides aiSIEM and aiXDR capabilities to help detect and investigate web exploit activity.
Organizations should investigate alerts promptly, identify affected applications and systems, contain confirmed threats, and remediate the underlying weakness. Depending on the incident and available integrations, response actions may include blocking malicious traffic, restricting compromised access, or isolating affected systems. Seceon's aiSIEM and aiXDR capabilities help security teams correlate suspicious activity, investigate potential web attacks, and support incident response.
Seceon’s AI-driven solution for Web Application Security monitors application traffic, detects vulnerabilities and malicious activities in real-time, and automatically blocks threats, ensuring robust protection against web-based attacks and application exploits.
Copyright @Seceon Inc 2026. All Rights Reserved.
